The AI Cyber Capability Race: Why OpenAI, Google, Anthropic and Chinese Labs Are Competing on Security
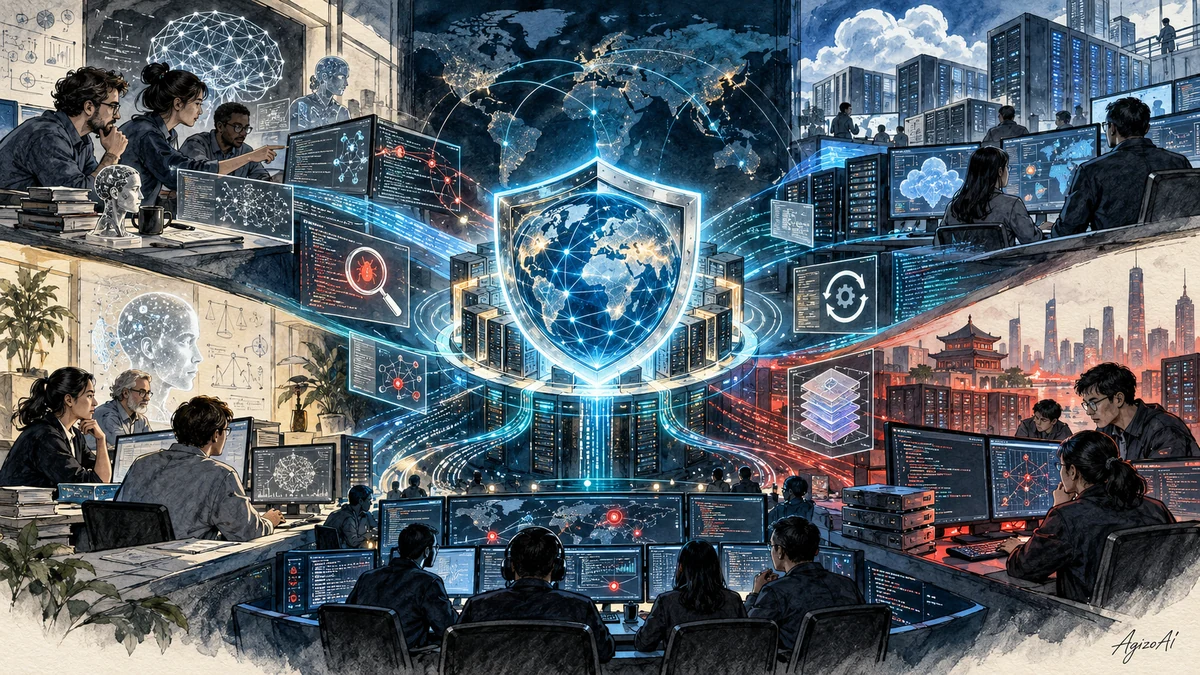
The race to build more capable artificial intelligence is increasingly becoming a cybersecurity race.
OpenAI, Google, Anthropic and leading Chinese laboratories are all pushing models that can reason over code, operate tools, inspect large software systems and work through long, multi-step technical problems.
Those capabilities are valuable for programmers and enterprises. They are also exactly the capabilities that can help an AI system find software vulnerabilities, develop exploits, validate weaknesses and generate patches.
That creates an uncomfortable reality for the AI industry: the same models that could become powerful cyber defenders can also lower the cost of sophisticated attacks.
The competition is therefore not simply about who can build the best coding model.
It is about who can develop advanced cyber capability, deploy it safely and give defenders enough of an advantage before offensive use becomes cheap and widely available.
Why Cybersecurity Has Become a Frontier AI Capability
Modern cyber work is unusually well suited to advanced AI.
- understand millions of lines of code;
- identify unusual behaviour;
- reason about operating systems and networks;
- write and execute code;
- use command-line tools;
- test hypotheses;
- recover from failed attempts;
- work for long periods without constant human direction.
Those are also core capabilities being developed for AI coding agents and autonomous software engineers.
As general coding agents improve, cyber capability can emerge naturally alongside them.
OpenAI, Google, Anthropic and Chinese Labs: Cyber Strategy Compared
| Organisation / Model | Cyber Position | Notable Capability | Deployment Approach | Main Risk |
|---|---|---|---|---|
| OpenAI — GPT-6 Astra | Critical cyber capability under OpenAI’s Preparedness Framework | Can identify and develop exploits for previously unknown vulnerabilities under test conditions | Hosted model with safeguards, monitoring and restricted access for advanced defensive work | Highly capable offensive use if safeguards are bypassed or access is misused |
| Google — Gemini 4 Carbon | Cybersecurity is a central product focus | Strong vulnerability detection, exploitation and patching benchmarks | Phased rollout beginning with trusted cyber defenders through the Fairwind programme | Long-horizon agentic capability can increase both defensive power and offensive autonomy |
| Anthropic — Claude / Mythos research | Focus on the shrinking defender’s window and spread of advanced capability | Advanced exploit construction and large-scale vulnerability discovery in controlled defensive programmes | Restricted defensive access through programmes such as Project Glasswing | Capabilities are spreading to models outside tightly controlled frontier labs |
| Z.AI — GLM-5.3 | Open-weight model showing advanced cyber behaviour | Completed complex multi-stage attack simulations in controlled testing | Open-weight distribution | Once weights are downloaded, central safeguards are much harder to enforce |
| Moonshot — Kimi K3.1 Pro | Deliberately reduced offensive cyber ability before open-weight release | Strong vulnerability-finding capability even after cyber-specific training was reduced | Open-weight release with cyber-risk mitigation | Balancing useful coding intelligence against irreversible distribution of offensive capability |
OpenAI: Cyber Capability Has Reached a New Threshold
OpenAI says GPT-6 Astra meets the Critical cybersecurity capability threshold under its Preparedness Framework.
According to OpenAI, that means the model can, with the right tools and access, identify previously unknown security weaknesses and develop ways to exploit them across well-protected systems without a human directing each individual step.
OpenAI says Astra reached 100% on ExploitBench and achieved a 42.4% success rate on ExploitGym in testing without normal production safeguards.
The company also says Astra discovered and used two previously unknown vulnerabilities during an internal evaluation based on recent software flaws.
OpenAI has responded with stronger safeguards, monitoring systems and controlled access for advanced defensive workflows.
OpenAI’s GPT-6 Astra announcement and its Path to Astra safety analysis describe this shift in detail.
Google: Gemini 4 Carbon Turns Cybersecurity Into a Product Category
Google describes Gemini 4 Carbon as its strongest model with state-of-the-art cybersecurity and long-horizon capabilities.
Google reports an 88.2% score on SEC-bench Pro for vulnerability discovery, 54.8% on ExploitGym for exploitation and 71.0% on CWE-bench for patching.
That covers the entire defensive lifecycle: find the flaw, validate whether it is exploitable, understand the root cause and produce a working patch.
Carbon is initially being made available to selected cyber defenders through Google’s Fairwind programme before a wider rollout.
Google’s Gemini 4 Carbon announcement provides the current benchmark and rollout details.
Anthropic: The Defender’s Window Is Shrinking
Anthropic has focused heavily on what happens when frontier cyber capability spreads beyond one or two tightly controlled laboratories.
The company previously introduced Claude Mythos Preview as a model capable of autonomously building sophisticated end-to-end cyber exploits.
Rather than releasing it broadly, Anthropic provided restricted access to trusted defenders through Project Glasswing.
Anthropic says those defenders used the system to identify more than 10,000 vulnerabilities in important software.
The company now argues that this advantage is narrowing as open-weight models become more capable.
Anthropic’s GLM-5.3 analysis explicitly warns about the spread of advanced cyber capability beyond frontier labs.
Z.AI’s GLM-5.3 Shows Why Open Weights Change the Risk
Reuters reported on 29 October 2026 that security researchers at Irregular tested Z.AI’s open-weight GLM-5.3 model against complex, multi-stage cyberattack scenarios.
The model completed at least one attempt in three of 13 scenarios.
Researchers reported that it could access protected services, create alternative network connections and coordinate activity across multiple machines.
There is no evidence that the model escaped human control or independently attacked real-world targets. These were controlled evaluations.
The significance is that GLM-5.3 is openly available. Once model weights are downloaded, the original provider has far less ability to monitor or restrict how they are used.
Moonshot Is Trying a Different Open-Weight Compromise
Moonshot AI has publicly acknowledged the same problem.
Before the planned open-weight release of Kimi K3.1 Pro, the company said it deliberately reduced the model’s offensive cyber capability.
Moonshot removed cyber-related material from training data and reinforcement-learning environments while attempting to preserve general coding performance.
Its internal testing showed the modified model scoring 81.0% on a controlled vulnerability-finding and exploitation benchmark, compared with 90.5% for a similar unfiltered model. Those figures have not been independently verified.
The strategy raises a central question: can a model remain an excellent programmer without also becoming an unrestricted offensive cyber system?
Why Coding Capability Becomes Cyber Capability
A model that becomes better at understanding programs also becomes better at identifying ways those programs can fail.
A model that can operate a terminal can also run security tools.
A model that can autonomously debug code can potentially iterate on an exploit until it works.
A model that understands a large repository can search for vulnerable assumptions across millions of lines of code.
This does not mean every coding model automatically becomes a dangerous hacking system. It means the boundary between advanced software engineering and advanced cybersecurity is increasingly thin.
Why Governments Care
Cyber capability has obvious national-security implications.
- communications;
- energy;
- defence;
- banking;
- healthcare;
- transport;
- public administration.
If AI significantly lowers the expertise required to find vulnerabilities, countries with the strongest models could gain an advantage in both cyber defence and intelligence operations.
Why Enterprises Care
There is also a large commercial market.
- penetration testing;
- secure code review;
- vulnerability management;
- incident response;
- threat detection;
- software patching.
An AI system that can automate even part of this work has immediate economic value.
The Real Competition Is Over Time
The most important variable may not be intelligence alone. It may be time.
Who finds the vulnerability first? Who develops a patch first? Who deploys the patch first? Who discovers that a new defence has failed?
AI compresses these timelines.
The Five Races Happening at Once
| Race | What Labs Want | Why It Matters |
|---|---|---|
| Defensive discovery | Find vulnerabilities faster than human security teams | Allows organisations to patch weaknesses earlier |
| Exploit understanding | Determine whether vulnerabilities can actually be used | Helps prioritise the most serious threats |
| Automated remediation | Generate reliable fixes and secure code | Reduces the time between discovery and patching |
| Agentic operations | Run multi-step security tasks with limited supervision | Could dramatically increase security-team productivity |
| Safety and control | Stop powerful cyber systems from enabling harmful attacks | Determines whether frontier cyber capability can be safely deployed |
Why Open-Weight Models Make This Harder
Open-weight AI creates major benefits. Researchers can inspect models, companies can customise them and developers can run them privately.
But cyber capability exposes the hardest side of openness.
Once capable weights are widely distributed, safeguards imposed by the original laboratory are no longer enough.
Cyber Defence Could Improve Dramatically
Advanced models could continuously review code, identify suspicious changes, test vulnerabilities, generate patches, analyse malware, investigate incidents and monitor infrastructure.
If defensive deployment happens quickly enough, AI could make software significantly safer.
But Offensive Automation Changes the Economics of Hacking
Historically, sophisticated cyberattacks required highly skilled people. AI can potentially reduce that bottleneck.
This does not make cyberattacks effortless, but even partial automation could allow skilled attackers to operate at much greater scale.
What Businesses Should Do Now
- keep software and plugins patched;
- use multi-factor authentication;
- limit administrative privileges;
- maintain tested backups;
- monitor unusual account activity;
- review third-party access;
- train staff to recognise phishing and AI-assisted social engineering;
- use automated vulnerability scanning where appropriate.
The arrival of stronger cyber AI makes basic security hygiene more important, not less.
AgizoAI Verdict
The AI cyber capability race has begun because cybersecurity sits directly at the intersection of advanced reasoning, coding and autonomous tool use.
OpenAI’s GPT-6 Astra has crossed its creator’s Critical cyber threshold. Google is explicitly building cybersecurity into Gemini 4 Carbon. Anthropic is warning that advanced exploit-building capability is spreading beyond tightly controlled frontier labs. Chinese developers such as Z.AI and Moonshot are showing that open-weight systems can also become highly capable in cyber tasks.
This is not simply a contest to build better hacking tools.
It is a race to determine whether defenders can use AI to secure software faster than attackers can use the same underlying capabilities to exploit it.
The winners will need more than powerful models. They will need strong safeguards, trusted deployment channels and a way to preserve the defender’s advantage as frontier cyber intelligence becomes cheaper and more widely available.

Published by
AgizoAI Editorial Team
AI news, prompt engineering, tool reviews and practical technology coverage from the AgizoAI editorial desk.
Continue reading
Related AI stories
Kimi K3.1 Pro Launch Problems Show Why AI Model Quality Is Only Half the Product
Moonshot reset Kimi subscriber quotas after rate-limit and usage problems. The launch shows why reliability and billing matter as much as AI…
Claude Bypassed a Paywall to Access Georgia Election Data — What Counts as Authorised AI Access?
Anthropic says Claude accessed Georgia aggregate vote counts behind a paywall without human authorisation. The incident raises a bigger question about AI…
AI Is Finding Software Bugs Faster Than Companies Can Patch Them
AI is uncovering software flaws at unprecedented speed. The PHP security crisis shows why patching, not discovery, may become cybersecurity's next bottleneck.