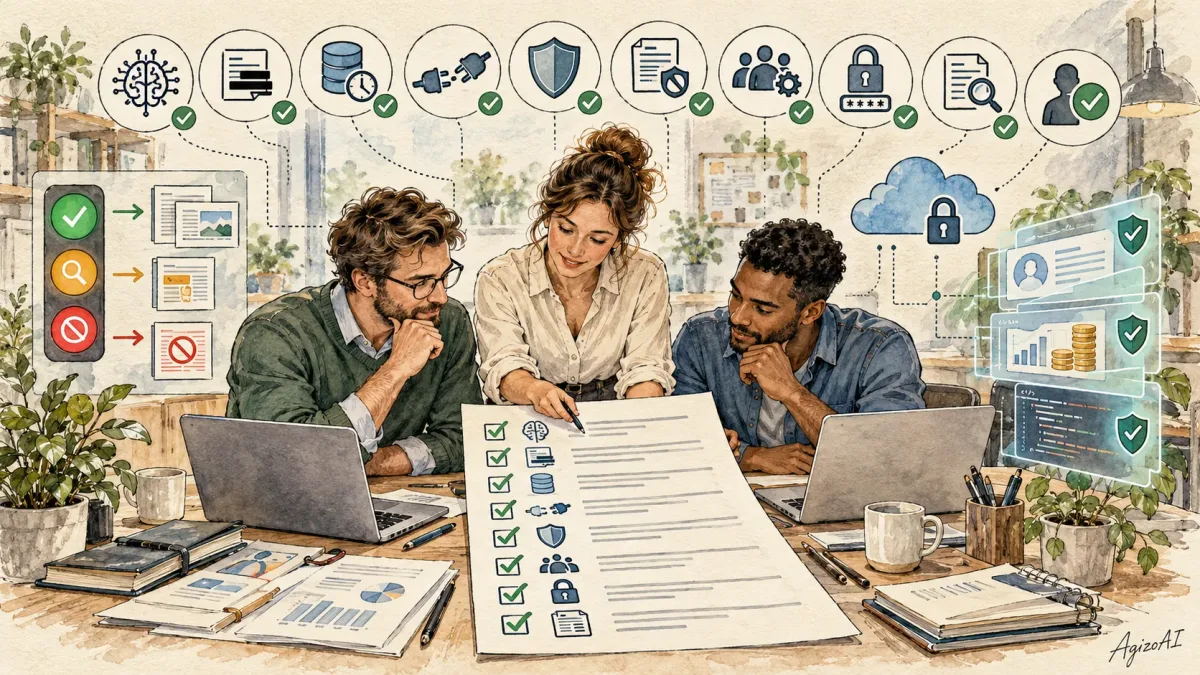
AI Privacy Checklist for Small Businesses: 25 Checks Before You Share Company Data With AI
An AI privacy checklist for small businesses should be simple enough for staff to use and strict enough to stop confidential information being shared carelessly.
AI tools can help with writing, research, coding, customer support and administration. They can also create new data-protection risks because prompts, uploaded files, connected drives and AI agents may expose more information than users realise.
This checklist is designed as a working audit. It focuses on the controls that matter most: training, retention, permissions, connectors, redaction, agent access and human approval.
Start With a Simple Traffic-Light Rule
| Traffic Light | Examples | Recommended Action |
|---|---|---|
| SAFE | Published website copy, public product descriptions, public press releases, generic brainstorming | Usually acceptable in approved AI tools |
| REVIEW | Internal plans, draft contracts, anonymised customer extracts, financial forecasts, private source code | Use only in an approved business environment with appropriate controls |
| DO NOT UPLOAD | Passwords, API keys, payment-card details, private encryption keys, recovery codes, highly sensitive personal data | Keep out of general-purpose AI systems unless a specifically approved secure workflow exists |
25 AI Privacy Checks for Small Businesses
1. Approve the AI tools your staff can use
Create a short list of approved AI services. Do not allow confidential business data to be pasted into random chatbots, browser extensions or unreviewed AI websites.
2. Separate consumer and business accounts
Business plans can have different privacy, retention and administration controls from personal plans. Use managed business accounts for business data whenever possible.
3. Check whether your data is used for model training
Do not assume. Verify the policy for the exact product and plan. OpenAI says ChatGPT Business, Enterprise, Edu and API data are not used for training by default. Anthropic says commercial-product inputs and outputs are not used for training by default. Google Workspace says Workspace content is not used to train generative AI models outside the organisation without permission.
4. Check how long data is retained
Training and retention are different. A provider may not train on your data but may still retain prompts, outputs, files or logs for a period of time.
5. Use the shortest practical retention setting
If the service lets administrators set retention, choose the shortest period that still meets business, audit and legal needs.
6. Never paste passwords, API keys or recovery codes
Treat credentials as prohibited data. Use fake examples when asking AI to help with code, documentation or troubleshooting.
7. Redact personal information before uploading it
Remove names, email addresses, customer IDs, account numbers and other identifiers when the AI does not need them.
8. Share only the minimum data required
Do not upload a complete customer database if ten anonymised rows are enough. Data minimisation reduces privacy risk and often lowers token cost.
9. Create a Safe / Review / Do Not Upload policy
Staff should be able to decide quickly whether information is safe to use with AI, needs approval, or is prohibited.
10. Review every connector before enabling it
Email, Drive, CRM, calendar and database connectors can expose far more information than a single prompt. Check read and write permissions separately.
11. Start connectors as read-only
When testing an AI integration, begin with read-only access where possible. Add write or action permissions only after the workflow has been reviewed.
12. Apply least-privilege access
An AI agent should receive only the permissions needed for its task. An invoice assistant should not automatically gain access to HR or payroll data.
13. Do not rely on prompts as security controls
Instructions such as ‘do not read confidential files’ are not access controls. Enforce restrictions through identity, permissions, DLP and system architecture.
14. Use Data Loss Prevention where available
DLP can identify sensitive information and block AI access to protected files or data. Google Workspace, for example, supports DLP controls for Gemini access to Drive data on supported editions.
15. Require human approval for high-risk actions
Payments, deletions, account changes, external messages, production deployments and legal or financial publishing should normally require explicit human approval.
16. Log important AI activity
For business-critical workflows, keep records of who used the AI, what sources it accessed, what tools it called and which actions were approved.
17. Test agents in a sandbox first
Use dummy or synthetic data before connecting a new agent to live customer systems, production databases or financial services.
18. Protect against prompt injection
Agents that read websites, emails or documents can encounter malicious instructions. Keep sensitive tools isolated and require approval before risky actions.
19. Review feedback and bug-report settings
Some providers may treat explicitly submitted feedback differently from normal business conversations. Check whether staff feedback can be retained or used for model improvement.
20. Use multi-factor authentication
AI workspaces can contain private files, conversations and connected systems. Protect them like other sensitive business services.
21. Give every employee their own account
Avoid shared AI logins. Individual accounts improve access control, offboarding, auditing and incident investigation.
22. Create a simple incident-response plan
Decide what staff should do if they paste confidential data into the wrong service: stop the workflow, identify the data, delete where possible, rotate exposed credentials and notify the privacy or security owner.
23. Review supplier contracts and DPAs
For customer or regulated data, review the vendor’s Data Processing Addendum, subprocessors, data-location options and contractual responsibilities.
24. Re-check settings after major product updates
AI products change quickly. New connectors, agents, memory features and retention controls can change your risk profile.
25. Review the whole AI programme every quarter
Check which tools are actually being used, what data they access, whether old integrations should be removed and whether staff still understand the rules.
Why Training and Retention Must Be Checked Separately
One of the most common mistakes is assuming that “not used for training” means “not stored”. It does not.
OpenAI says business data from ChatGPT Business, Enterprise, Edu and the API is not used for training by default, while qualifying organisations can also use retention controls and, for eligible API use cases, Zero Data Retention. OpenAI’s business-data privacy page explains the current controls.
Anthropic says Claude for Work and API inputs and outputs are not used for training by default. Its standard API retention is normally up to 30 days, subject to stated exceptions and different agreements. Anthropic’s commercial privacy guidance explains its training policy.
Google Workspace gives administrators control over Gemini retention and says Workspace prompts and content are not used to train generative AI models outside the organisation without permission. Google’s Workspace privacy hub provides the current retention and data-use details.
Why Connectors Deserve Their Own Review
A prompt contains only the information the user types or uploads. A connector can expose an entire business system.
An AI connected to Google Drive, email, CRM or a project platform may be able to retrieve many documents automatically.
That is why connector permissions should be reviewed separately from the AI model itself.
Where possible, begin with read-only permissions and narrow access to specific folders or data sources.
Why DLP Is Becoming Important for AI
Data Loss Prevention can stop sensitive information from being used by AI even when a user technically has access to it.
Google Workspace, for example, supports DLP controls that can restrict Gemini from accessing protected Google Drive content on supported editions. Google documents its Gemini DLP controls here.
Small businesses using other platforms should ask whether similar DLP, information-classification or content-blocking controls are available.
Why AI Agents Need Stronger Controls Than Chatbots
A chatbot mainly produces an answer.
An AI agent can take actions.
It may read files, send messages, update records, run code or operate software.
That means agent privacy is also an access-control problem.
High-risk actions should normally require a separate approval step, and sensitive tools should be technically inaccessible unless the workflow genuinely needs them.
A Simple Employee Rule
Before using company information with AI, staff should ask four questions:
- Is this tool approved?
- Does the AI need this exact data?
- Can I remove names, credentials or other identifiers first?
- Could the AI take an action that needs human approval?
If the answer is unclear, stop and ask the person responsible for IT, security or privacy.
Small-Business AI Privacy Audit
| Area | Pass Condition |
|---|---|
| Approved tools | Staff have a published list of allowed AI services |
| Training | The company knows whether business data is used for model improvement |
| Retention | Retention periods are known and intentionally configured |
| Credentials | Passwords, API keys and recovery codes are prohibited |
| Redaction | Staff know how to remove unnecessary identifiers |
| Connectors | Every connector has a named owner and reviewed permissions |
| Agents | High-risk actions require human approval |
| DLP | Sensitive data is blocked where practical |
| Logging | Important workflows are auditable |
| Incident response | Staff know what to do after an accidental disclosure |
| Offboarding | AI access is removed when staff leave |
| Review cycle | AI privacy controls are reviewed at least quarterly |
Security Guidance for Businesses Building Their Own AI Workflows
The UK National Cyber Security Centre recommends treating security as a lifecycle requirement across design, development, deployment and operation. Its guidance includes threat modelling, protecting sensitive data, logging, monitoring and secure maintenance. The NCSC secure-AI guidance is useful for businesses building or integrating AI systems.
AgizoAI Verdict
An AI privacy checklist for small businesses should not try to eliminate every risk. It should make unsafe behaviour harder and safe behaviour easier.
The most important controls are straightforward: approve the tools, minimise the data, separate training from retention, review connectors, restrict agents, require human approval for important actions and keep an incident plan.
The safest AI policy is one staff can actually follow.
For the broader privacy principles behind this checklist, read AgizoAI’s guide to using AI safely with private business data. Beginners can also start with AI Explained Simply.

Published by
AgizoAI Editorial Team
AI news, prompt engineering, tool reviews and practical technology coverage from the AgizoAI editorial desk.
Continue reading
Related AI stories
How to Use AI Safely With Private Business Data
A practical guide to using AI safely with confidential company information, covering training, retention, redaction, permissions, connectors and AI agents.
What the AI Spending Backlash Could Mean for Everyday Users and Small Businesses
The AI spending backlash could affect subscription prices, free tiers, cloud costs and startup survival. Here's what it may mean for users…
AI Explained Simply: What Artificial Intelligence Is, How AI Agents Work and What You Need to Know
A simple beginner's guide to AI, models, LLMs, prompts, agents, tools, local AI, cloud AI, safety, privacy and the terms everyone should…