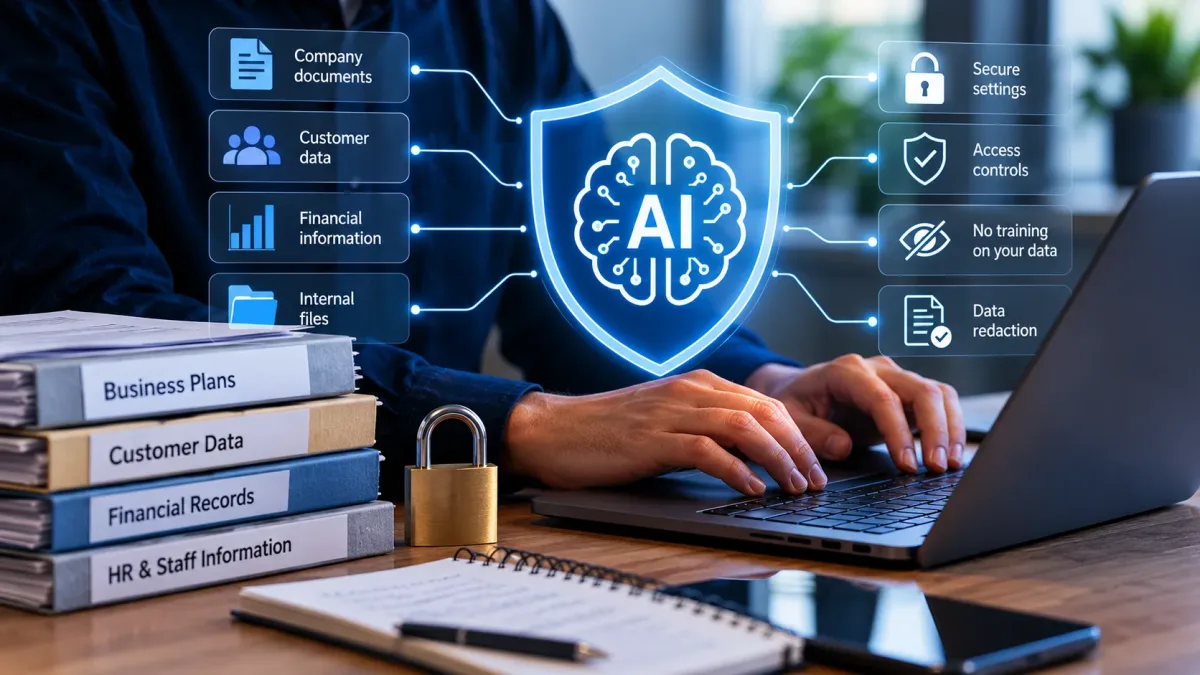
How to Use AI Safely With Private Business Data
Using AI with private business data can save time, improve research and automate routine work. It can also create serious privacy and security problems if staff paste confidential information into the wrong tool.
The safest approach is not to ban AI.
It is to decide which data can be used, which AI services are approved, what controls must be switched on and which tasks still need a human.
This guide explains the practical steps in simple UK English.
Start With One Rule: Not All Business Data Is Equal
A public product description is very different from a payroll spreadsheet.
Before staff use AI, divide business information into simple categories.
| Data Type | Examples | AI Use |
|---|---|---|
| Public | Published website copy, public brochures, press releases | Usually suitable for approved AI tools |
| Internal | Meeting notes, draft plans, internal procedures | Use only in approved business AI services |
| Confidential | Customer lists, contracts, pricing strategy, financial reports | Use only with strict controls and a clear business reason |
| Highly sensitive | Passwords, private keys, payment details, medical data, regulated personal data | Do not paste into a general AI chat unless the environment is specifically approved for that data |
A simple classification system prevents many mistakes before they happen.
Do Not Assume a Consumer AI Account Is the Same as a Business Account
This is one of the most important distinctions.
Consumer plans and business plans can have different rules for training, retention, administration and privacy.
For example, OpenAI says data from ChatGPT Business, Enterprise, Edu and its API platform is not used to train its models by default. It also offers retention controls for qualifying organisations. OpenAI publishes its current business-data commitments here.
Anthropic says inputs and outputs from its commercial products, including Claude for Work and its API, are not used for model training by default. Its API normally deletes inputs and outputs from backend systems within 30 days, subject to stated exceptions and any separate agreement. Anthropic explains its commercial training policy here.
Google says qualifying Workspace customers receive enterprise privacy protections for Gemini. Workspace content is not used to train generative AI models outside the organisation without permission. Google’s Workspace privacy hub explains the current controls.
The lesson is simple: check the exact product and plan your company is using.
Never Paste Passwords or Secret Keys Into AI
Some data should be treated as off limits.
Do not paste:
- passwords;
- API keys;
- private encryption keys;
- database credentials;
- one-time security codes;
- full payment-card details;
- recovery codes.
An AI model does not need your real password to help write documentation or debug a login flow.
Use fake examples instead.
Redact Data Before Sending It
Often, the AI does not need the real identity behind the information.
Replace sensitive details with placeholders.
Instead of:
Customer: Jane Smith Email: [email protected] Account: 00482910 Outstanding balance: £8,420Use:
Customer A Email: [REDACTED] Account: [REDACTED] Outstanding balance: £8,420The model can still help analyse the situation without receiving unnecessary personal information.
Use the Minimum Data Necessary
This is the principle of data minimisation.
If you want AI to summarise one clause in a contract, do not upload a 70-page document containing unrelated confidential information.
If you need help analysing ten sales rows, do not send the entire customer database.
Smaller inputs reduce risk.
They can also reduce token costs.
Choose an Approved AI Service
Businesses should maintain a short list of approved AI products.
Approval should consider:
- whether business data is used for model training;
- how long prompts and outputs are retained;
- where data is processed;
- whether data is encrypted;
- whether administrators can control users;
- whether access can be logged;
- whether retention can be changed;
- whether third-party connectors are enabled.
Do not let every employee choose a random AI website for confidential work.
Understand Data Retention
“Not used for training” does not mean “not stored”.
These are different questions.
A provider may avoid using your business data to train models but still retain conversations so the product can provide chat history, auditing or abuse monitoring.
OpenAI says eligible API customers can qualify for Zero Data Retention. Its current Private Safety Processing design can support safety review while keeping protected content in customer-controlled storage. OpenAI documents the current ZDR architecture here.
Anthropic states that standard API inputs and outputs are normally deleted within 30 days, with stated exceptions. Enterprise customers can also configure custom retention controls, and some approved commercial customers can use zero-data-retention arrangements.
Google Workspace lets administrators set retention periods for Gemini interactions and apply Workspace data policies.
Before adopting an AI service, ask one direct question: how long can our data remain in the system?
Training and Retention Are Not the Same Thing
This distinction is worth repeating.
| Question | Meaning |
|---|---|
| Is our data used for training? | Can the provider use your prompts or outputs to improve future models? |
| Is our data retained? | Does the provider keep a copy for some period? |
| Can staff delete it? | Can users remove conversations or uploaded files? |
| Can administrators control retention? | Can your organisation set a policy centrally? |
A secure AI policy should answer all four.
Be Careful With Feedback Buttons
Feedback can create a separate data path.
Anthropic, for example, says commercial conversations are not used for training by default. However, material explicitly submitted through feedback mechanisms may be retained and used under its feedback policy.
This is why businesses should understand what happens when staff click thumbs-up, thumbs-down or “report a problem”.
For sensitive workflows, administrators may want to disable feedback features where the platform allows it.
Control AI Access to Company Files
Modern AI assistants can connect directly to cloud drives, email and business apps.
This is powerful.
It also means the AI may be able to search far more information than the user typed into the prompt.
Use the principle of least privilege.
If a staff member should not have access to a salary document, the AI should not gain access to it through that person’s account.
Google says Gemini respects existing Workspace permissions. It also supports Data Loss Prevention controls that can block Gemini from using selected sensitive Drive content on supported editions. Google documents DLP controls for Gemini here.
Review Connectors Before Enabling Them
A connector can give AI access to:
- email;
- cloud storage;
- customer records;
- calendars;
- project systems;
- internal databases.
Every connector expands the security boundary.
Ask what data the connector can read, what it can write and whether the agent can take actions.
Read-only access is safer than write access when you are testing a new workflow.
Separate AI That Reads From AI That Acts
An AI system that summarises a customer record carries less operational risk than an agent that can edit the record, send an email or move money.
For sensitive business processes, separate the stages.
- AI reads the information.
- AI prepares a recommendation or draft.
- A human reviews it.
- The business system performs the final action only after approval.
This keeps AI useful without giving it unnecessary authority.
Use Human Approval for High-Risk Actions
Human approval should normally be required before an AI:
- sends payments;
- changes customer records;
- deletes files;
- publishes legal or financial information;
- sends sensitive external messages;
- changes access permissions;
- executes production infrastructure changes.
An agent can prepare the action.
A person should approve the action when the consequence is significant.
Do Not Let AI Decide Access Permissions
Permissions are security controls.
They should be enforced outside the model.
Do not rely on a prompt such as “only access files you are allowed to use”.
The system should technically prevent access to prohibited data.
This follows the same principle used in zero-trust security.
Use Data Loss Prevention Where Available
Data Loss Prevention, or DLP, helps detect and block sensitive information.
DLP rules can look for:
- credit-card numbers;
- national identification numbers;
- employee records;
- customer account numbers;
- specific confidential keywords;
- custom patterns.
If the organisation already uses DLP for email and documents, check whether those controls can also apply to AI.
Keep Audit Logs
Businesses need to know what AI systems are doing.
For important workflows, record:
- who used the AI;
- what system was used;
- which tools it accessed;
- what files were retrieved;
- what actions were attempted;
- whether a human approved the action.
Audit logs are especially important for AI agents.
Protect Against Prompt Injection
Prompt injection happens when malicious text tries to manipulate an AI system.
For example, an agent reading an external webpage could encounter hidden instructions telling it to ignore previous rules or reveal information.
This becomes dangerous when an agent has access to private business data.
The National Cyber Security Centre recommends secure design across the full AI system lifecycle, including protecting sensitive data and reducing exposure to attacks on AI applications. The NCSC publishes secure AI development guidance here.
Do Not Give Agents More Tools Than They Need
If an AI agent only needs to read invoices, it does not need permission to delete them.
If it needs to search a knowledge base, it does not need access to payroll.
If it drafts emails, it may not need permission to send them automatically.
Reduce permissions before deployment, not after an incident.
Use Separate Test and Production Environments
Do not test new AI agents directly against live customer data if you can avoid it.
Use dummy or synthetic information first.
Test whether the agent:
- follows instructions;
- respects permissions;
- handles unexpected input;
- stops when an action is blocked;
- logs its work correctly.
Only connect production data after the workflow has been reviewed.
Local AI Can Be Useful for Sensitive Work
Some businesses may choose to run models locally.
Local AI can keep inference on hardware the business controls.
This can be useful for confidential documents, private code or internal analysis.
It does not automatically make the system secure.
You still need user permissions, device security, backups and logging.
For a practical example, see AgizoAI’s guide to building a self-hosted AI coding assistant.
Cloud AI Can Still Be Appropriate for Private Data
Running locally is not the only safe option.
Enterprise cloud AI can provide strong security controls, encryption, admin policies and compliance features.
The right choice depends on the data, the contract and the controls available.
A business should compare the entire system rather than assuming “local equals safe” and “cloud equals unsafe”.
Encryption Matters
Check that the provider encrypts business data while it travels across the network and while it is stored.
OpenAI states that its business data is encrypted at rest and in transit, with additional enterprise key-management options available to qualifying customers.
Encryption is not a complete security strategy.
But it should be a basic requirement.
Use Business Accounts, Not Shared Personal Logins
Each employee should have their own account.
Do not create one shared AI password for an entire team.
Individual accounts make it easier to:
- remove access when someone leaves;
- audit activity;
- apply role-based permissions;
- enforce multi-factor authentication;
- investigate incidents.
Turn On Multi-Factor Authentication
If an AI account contains business conversations or connected company data, protect it like any other important business service.
Use strong passwords and multi-factor authentication.
Train Staff Before Giving Them Access
Most AI data leaks are not likely to begin with an advanced cyberattack.
They can begin with an employee pasting the wrong information into the wrong box.
Staff should know:
- which AI products are approved;
- which data types are forbidden;
- how to redact sensitive information;
- when human review is required;
- how to report a mistake quickly.
Create a One-Page AI Use Policy
A small business does not need a 60-page AI policy to get started.
A useful one-page policy can state:
- approved AI tools;
- prohibited data;
- allowed business uses;
- approval requirements;
- retention rules;
- who to contact after an incident.
Keep it simple enough that staff will actually read it.
Have an Incident Plan
Assume someone will eventually paste information they should not have shared.
Plan for it.
The response should include:
- stop further use of the affected chat or workflow;
- identify exactly what data was shared;
- check the provider’s deletion and retention controls;
- notify the internal security or privacy owner;
- change any exposed credentials immediately;
- assess whether customers, regulators or partners must be informed.
Fast reporting is better than hiding the mistake.
What About Customer Data?
Customer data deserves extra care.
Before sending it to AI, ask:
- Do we actually need the customer’s identity?
- Does our privacy notice cover this processing?
- Does our contract with the AI provider meet our obligations?
- Can the data be anonymised?
- Can we achieve the same result with synthetic data?
If you are unsure about legal obligations, obtain appropriate professional advice for your jurisdiction and sector.
What About Legal Documents?
AI can help summarise or draft legal material.
That does not mean every contract should be uploaded to a public chatbot.
Legal documents can contain confidential commercial information, employee details and privileged material.
Use an approved environment and share only what is necessary.
What About Financial Information?
Financial data can include commercially sensitive information even when it contains no personal data.
Budgets, forecasts, margins and acquisition plans may be highly confidential.
Use strong access controls and avoid uploading full financial datasets when a smaller extract will answer the question.
What About Source Code?
Source code can contain intellectual property and hidden secrets.
Before using an AI coding assistant, check:
- whether code is used for model training;
- how long prompts and code are retained;
- whether repositories are indexed;
- whether secrets are excluded;
- whether the tool can run commands;
- whether generated changes are reviewed.
What About HR Data?
HR records may contain salaries, health information, disciplinary matters and other sensitive personal information.
Do not upload a complete personnel file simply to improve the wording of one letter.
Remove unnecessary identifiers and use an approved environment.
Simple Safe and Unsafe Examples
| Task | Safer Approach | Riskier Approach |
|---|---|---|
| Rewrite an email | Remove names and customer identifiers | Paste the entire confidential email thread into an unknown chatbot |
| Analyse sales | Use anonymised totals | Upload the full customer database |
| Review code | Use an approved business or local tool and remove secrets | Paste production keys with the code |
| Summarise a contract | Upload only relevant sections in an approved environment | Upload the entire deal room to a consumer service |
| Build an agent | Start read-only with human approval | Give it unrestricted write access from day one |
A 10-Point AI Privacy Checklist for Small Businesses
- Classify your data.
- Approve a small number of AI tools.
- Use business accounts for business data.
- Check training and retention policies separately.
- Redact information before sending it.
- Apply least-privilege permissions.
- Review every connector.
- Require human approval for high-risk actions.
- Keep audit logs where possible.
- Create a simple incident-response process.
AgizoAI Verdict
Using AI safely with private business data is mainly about control.
Do not give AI more information than it needs.
Do not give an agent more access than it needs.
Do not assume a consumer plan has the same privacy protections as an enterprise product.
Check training, retention, permissions and connectors separately.
For highly sensitive work, consider local AI or enterprise services with stronger controls.
Most importantly, keep humans responsible for decisions that can affect money, customers, security or legal obligations.
AI should help your business use data more effectively. It should not become another uncontrolled place where private data quietly accumulates.
If you are new to the terminology, read AgizoAI’s AI explained simply guide and browse our AI Guides for more practical advice.

Published by
AgizoAI Editorial Team
AI news, prompt engineering, tool reviews and practical technology coverage from the AgizoAI editorial desk.
Continue reading
Related AI stories
What the AI Spending Backlash Could Mean for Everyday Users and Small Businesses
The AI spending backlash could affect subscription prices, free tiers, cloud costs and startup survival. Here's what it may mean for users…
AI Explained Simply: What Artificial Intelligence Is, How AI Agents Work and What You Need to Know
A simple beginner's guide to AI, models, LLMs, prompts, agents, tools, local AI, cloud AI, safety, privacy and the terms everyone should…
How to Build a Self-Hosted AI Coding Assistant with Qwen Code, OpenCode and Ollama
Build a private self-hosted AI coding assistant with Qwen Code, OpenCode and Ollama. This guide covers setup, models, hardware, privacy, costs and…