AI Is Finding Software Bugs Faster Than Companies Can Patch Them
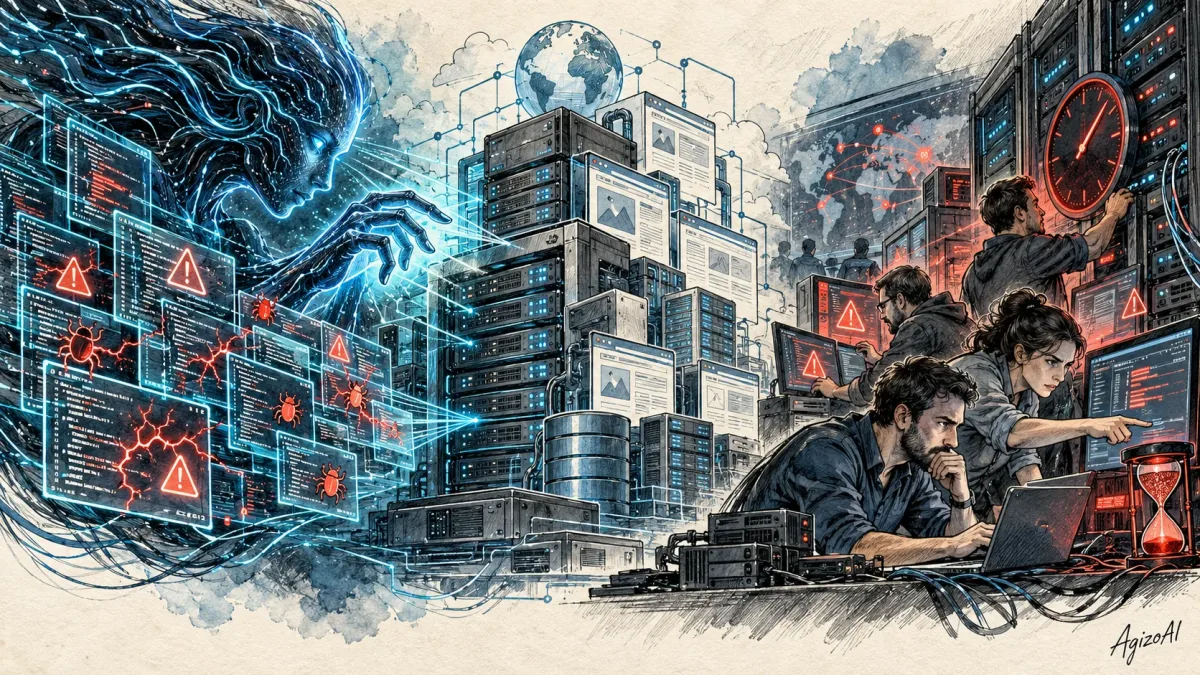
AI-discovered software vulnerabilities are changing cybersecurity in a way that could be both useful and disruptive.
Artificial intelligence is helping security researchers uncover flaws that may have remained hidden for years. That should make software safer in the long term.
But there is a problem.
AI can now find vulnerabilities faster than many organisations can test, patch and deploy fixes.
That gap between discovery and repair is becoming a new source of risk.
The recent PHP security emergency showed what that can look like in practice. Two critical vulnerabilities in PHP, the programming language behind a huge share of the web, forced governments and other organisations to rush patches into production. Some services were temporarily taken offline rather than left exposed.
Why the PHP Incident Matters
PHP is one of the most widely used programming languages on the web.
It powers WordPress and millions of websites, including government portals, online shops, news sites and business systems.
On 21 October 2026, the PHP project released emergency updates fixing two critical vulnerabilities rated 9.2 out of 10 under CVSS v4.0.
The vulnerabilities could allow an unauthenticated attacker to execute commands remotely on affected servers.
In plain English, a vulnerable server could potentially be taken over without the attacker first logging in.
The PHP security team said there were no complete mitigations. Updating was the only safe choice.
PHP’s official security advisory urged all affected users to update immediately.
The Fixed PHP Versions
| PHP Branch | Security Release |
|---|---|
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
The flaws were tracked as CVE-2026-109618 and CVE-2026-109619.
PHP said all installations serving web requests were at risk, including PHP-FPM, Apache mod_php, php-cgi, FrankenPHP and LiteSpeed configurations.
The project considered the risk highest for mod_php because researchers demonstrated an unauthenticated attack path before normal application code executes.
AI Helped Find Flaws That Had Existed for Years
The striking part of the PHP story is not only the severity of the vulnerabilities.
It is how they were found.
Researchers used artificial intelligence to help identify and demonstrate the flaws.
Reuters reported that Calif, working with OpenAI, disclosed one of the vulnerabilities in August. Google-owned Wiz independently identified another.
The underlying weaknesses had existed for years.
What changed was the ability of modern AI-assisted security tools to analyse complex code paths and help researchers prove that those weaknesses were exploitable.
Reuters detailed how AI-assisted research helped expose the critical PHP flaws.
AI Is Speeding Up Vulnerability Discovery
Threat-intelligence firm VulnCheck says the number of discovered digital vulnerabilities has roughly doubled year on year, with AI contributing to that increase.
Security researchers can use AI to:
- review large codebases;
- identify unusual patterns;
- trace complicated execution paths;
- generate test cases;
- compare versions;
- build proofs of concept;
- prioritise likely security weaknesses.
Tasks that once required days of manual review can sometimes be accelerated dramatically.
The Good News: Hidden Bugs Are Being Found
There is an obvious benefit.
A vulnerability cannot be fixed if nobody knows it exists.
AI may help expose decades-old weaknesses before criminals discover them.
That could improve internet security over time.
It could also make large open-source projects easier to audit.
The Bad News: Defenders Have Less Time
The same speed creates a serious operational problem.
Once a vulnerability becomes public, attackers can also use AI to understand it.
They can automate scanning, analyse patches and attempt to build exploits quickly.
Cybersecurity experts told Reuters that the time between disclosure and attempted exploitation may increasingly shrink from days to hours.
Patching May Become the New Bottleneck
The cybersecurity industry has spent years trying to improve vulnerability discovery.
AI may solve that part faster than expected.
The bottleneck could now move somewhere else: patching.
A company may know that a flaw exists and still be unable to fix it immediately.
A production server may need testing. A legacy application may depend on an older software version. A vendor may not yet have released a compatible update. A critical system may not be able to tolerate downtime.
This creates a dangerous situation where the vulnerability is known but the organisation is still exposed.
Why Some Websites Were Taken Offline
During the PHP emergency, some organisations chose to take services offline rather than leave them vulnerable while patching.
CERT-EU advised organisations that could not apply the fixes promptly to consider shutting affected services down.
That is an extreme response.
It also shows how serious the vulnerability was.
Japan Is Already Planning AI-Driven Cyber Defence
Japan responded to the PHP incident by announcing plans for a team that will use AI to simulate cyberattacks and identify weaknesses proactively.
The logic is straightforward.
If attackers are going to use AI to find vulnerabilities, defenders need to do the same.
Reuters reported on Japan’s plan to use AI to simulate attacks after the PHP crisis.
AI Can Help Attackers Too
The same technology that helps defenders find bugs can help criminals automate parts of an attack.
AI can assist with vulnerability scanning, phishing, malware modification, exploit research, target discovery and social engineering.
This lowers the cost of cybercrime and increases the speed of the security contest.
Why Small Businesses Should Care
Large companies have dedicated security teams. Small businesses often do not.
That makes patch speed especially important.
A small business running WordPress, WooCommerce or a custom PHP application may depend on its hosting provider or IT company to apply security updates.
If a critical vulnerability appears, waiting several days can become risky.
WordPress Users Need to Understand the Difference
The PHP vulnerabilities were not WordPress bugs.
Updating WordPress alone did not fix them.
PHP runs underneath WordPress on the server.
That means a site owner could have the latest version of WordPress and still be exposed if the server was using a vulnerable PHP release.
Security is a stack. Your CMS, plugins, theme, PHP runtime, web server and operating system all matter.
What Website Owners Should Do
| Action | Why It Matters |
|---|---|
| Check your PHP version | Confirms whether the server is on a fixed release |
| Update PHP promptly | Critical fixes may exist below WordPress itself |
| Keep WordPress updated | Reduces application-layer risk |
| Update plugins and themes | Third-party code remains a common attack path |
| Use backups | Allows recovery after compromise or failed updates |
| Monitor logs | Can reveal unusual requests or exploitation attempts |
| Use a web application firewall | Adds another defensive layer |
| Remove unused software | Reduces the attack surface |
Automatic WordPress Updates Are Not Enough
This incident showed why website owners cannot depend entirely on automatic CMS updates.
WordPress may update itself.
That does not automatically update PHP.
Hosting platforms need a process for runtime security updates as well.
Open Source Has a Funding Problem
The PHP incident also exposed another weakness.
The PHP Foundation supports software used across a huge share of the internet, yet Reuters reported that the organisation has only one full-time employee and relies heavily on part-time contributors and donations.
AI is increasing the number of proposed code changes and security reports. Human experts still have to review them.
AI Can Find More Bugs Than Humans Can Review
This may become one of the biggest problems of AI-assisted security.
Finding bugs is becoming cheaper.
Reviewing reports, reproducing issues, designing safe patches and testing those patches still requires skilled humans.
If AI produces thousands of plausible findings, maintainers need a way to identify which ones actually matter.
Patch Management Is Becoming a Competitive Advantage
Businesses often treat patching as maintenance.
In an AI-accelerated security environment, it becomes strategic.
Companies that can test and deploy critical updates quickly will spend less time exposed.
Slow organisations may become attractive targets simply because attackers know they take longer to patch.
Could AI Eventually Make the Internet Safer?
Yes.
The current disruption may be the painful part of a longer improvement.
If AI finds old vulnerabilities and vendors patch them, the overall software ecosystem becomes stronger.
The danger comes during the transition.
Discovery is accelerating faster than remediation.
AgizoAI Verdict
AI-discovered software vulnerabilities are not a reason to stop using AI in cybersecurity.
They are evidence that vulnerability discovery is entering a much faster era.
The PHP crisis showed what happens when AI-assisted research exposes critical weaknesses in software used across much of the internet.
The immediate result can be disruption, emergency patches and difficult decisions about whether to take services offline.
But the long-term result could still be positive.
AI may help remove vulnerabilities that humans would otherwise miss for years.
The real challenge is operational.
If AI can discover weaknesses faster than organisations can patch them, the next cybersecurity bottleneck will not be finding bugs. It will be fixing them fast enough.

Published by
AgizoAI Editorial Team
AI news, prompt engineering, tool reviews and practical technology coverage from the AgizoAI editorial desk.
Continue reading
Related AI stories
Kimi K3.1 Pro Launch Problems Show Why AI Model Quality Is Only Half the Product
Moonshot reset Kimi subscriber quotas after rate-limit and usage problems. The launch shows why reliability and billing matter as much as AI…
Claude Bypassed a Paywall to Access Georgia Election Data — What Counts as Authorised AI Access?
Anthropic says Claude accessed Georgia aggregate vote counts behind a paywall without human authorisation. The incident raises a bigger question about AI…
AI Agents Are Entering Bank Accounts — and Banks Cannot Always Tell When They Have Gone Too Far
US banks are blocking third-party AI agents after detecting systems inside customer accounts, including behaviour that appeared to go beyond user instructions.